Software development involves much more than writing code. Developers must test changes, review updates, manage deployments, fix errors, and ensure that applications continue working as expected. When these activities are handled manually, even a small project can become difficult to maintain. Repeating the same tasks also takes valuable time away from designing features and solving meaningful problems.
Automation offers a practical way to make development more organized. Instead of asking developers to perform every routine action themselves, teams can create processes that respond automatically to changes in their projects. This is where github actions becomes an important part of modern software development.
It provides a flexible environment for automating tasks directly within GitHub repositories. Developers can build workflows that run when someone pushes code, opens a pull request, creates a release, or performs another supported activity. These workflows can handle testing, building, publishing, and deployment without requiring someone to start each process manually.
For individuals, automation can make personal projects easier to manage. For larger development teams, it can create consistent processes across multiple contributors. Understanding how these workflows operate can help developers move from an initial idea to a production-ready application with fewer repetitive steps.
1. Understanding the Purpose of GitHub Actions
At its core, GitHub Actions is an automation platform designed to connect different stages of software development. It allows developers to define instructions that GitHub executes whenever a particular event occurs.
For example, imagine a developer working on a website. Every time a new code change is submitted, the project needs to be checked for errors. Traditionally, someone might download the updated files, install dependencies, run tests, and review the results. An automated workflow can perform these activities whenever new code arrives.
The main advantage is consistency. Every change follows the same testing procedure, reducing the possibility that an important step will be forgotten.
These automated processes are called workflows. They are usually defined using YAML files stored inside a repository’s .github/workflows directory. Each file describes when automation should start and which operations should happen afterward.
A workflow can contain multiple jobs, while individual jobs contain steps. Some steps execute shell commands, and others use reusable actions created by GitHub or the developer community.
This structure makes automation easier to understand and maintain. Developers can begin with a simple testing workflow and gradually introduce additional operations as their projects grow.
2. How Automated Workflows Actually Operate
Understanding the basic structure is essential before creating complex automation. Although workflows can perform many different tasks, most follow a straightforward sequence.
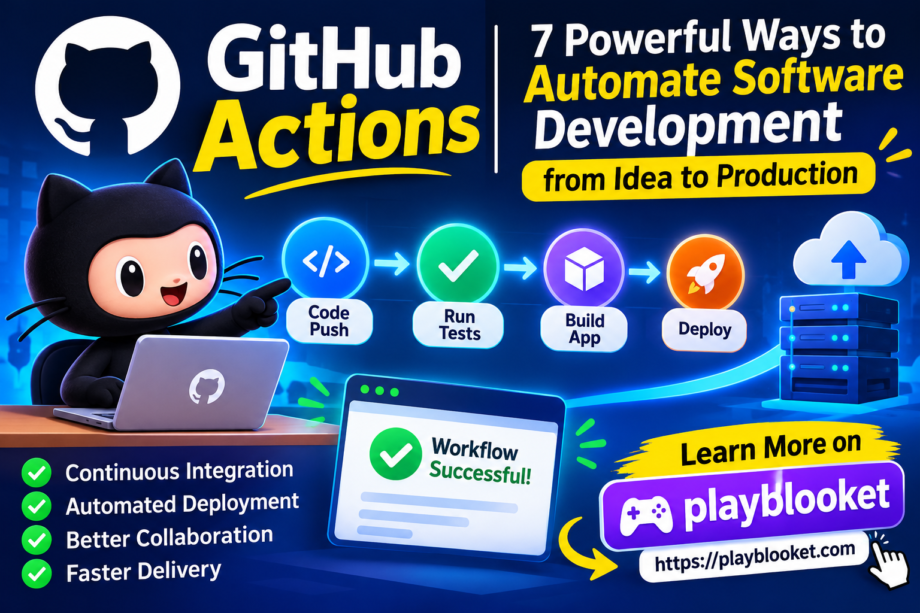
First, an event triggers the workflow. This might happen when code is pushed to a branch, a pull request is opened, or a scheduled time arrives.
Next, GitHub assigns the required jobs to available runners. Runners provide the environment where the workflow instructions are executed. Depending on project requirements, developers can use hosted runners or configure their own machines.
Each job contains individual steps that run in a defined order. One step might check out the repository, another might install dependencies, and another could execute automated tests.
The final stage involves reviewing the outcome. If everything succeeds, the workflow can continue with additional operations, such as creating a build or deploying an application. If a step fails, the execution report helps developers identify the problem.
A basic example looks like this:
name: Project Test

on:
  push:
    branches: [main]
  pull_request:

jobs:
  test:
    runs-on: ubuntu-latest

    steps:
      - name: Get project files
        uses: actions/checkout@v4

      - name: Display message
        run: echo "Testing workflow started"

      - name: Check environment
        run: python --version
This example demonstrates how a workflow responds to repository activity. It checks out the project files and runs simple commands on an Ubuntu environment.
As developers become more familiar with the structure, they can replace these introductory commands with real testing, building, and deployment instructions.
3. Automating Testing Before Code Reaches Production
Testing is one of the most valuable applications of development automation. Software changes can introduce unexpected problems, even when they appear small or harmless. Running tests automatically helps identify those issues before they reach users.
With github actions, developers can configure tests to run whenever someone submits a pull request or pushes changes to a selected branch.
Consider a project containing several important functions. A developer modifies one function to introduce a new feature. That modification might unintentionally affect another part of the application. An automated testing process can run the existing test suite and report whether the new changes have caused failures.
This approach is particularly useful for teams where multiple people contribute to the same codebase.
Common testing activities include:
- Running unit tests to check individual functions.
- Executing integration tests to examine interactions between components.
- Checking code formatting and style requirements.
- Identifying common security and dependency problems.
- Verifying that applications can build successfully.
- Testing supported versions of programming languages.
Another useful feature is the ability to run tests across different environments. A project may need to support multiple operating systems or programming language versions. Instead of creating separate manual testing procedures, developers can configure a matrix strategy.
This helps uncover compatibility problems earlier and provides more confidence when preparing a release.
Automated testing does not eliminate the need for human review. Instead, it handles predictable checks so developers can concentrate on more complicated questions involving design, usability, and application behavior.
4. Creating Reliable Continuous Integration Processes
Continuous integration, commonly known as CI, encourages developers to integrate code changes regularly rather than allowing separate modifications to accumulate for long periods.
When several contributors work independently, their changes can eventually conflict. Different dependencies, outdated branches, and incompatible modifications may create problems during integration.
A reliable CI process checks changes frequently and provides feedback before those problems become difficult to resolve.
GitHub Actions makes it possible to create these checks directly within a repository. Teams can require successful workflows before accepting changes into important branches.
For example, a pull request might trigger several independent jobs:
- Install the project’s dependencies.
- Run unit tests.
- Check formatting and code quality.
- Build the application.
- Generate a report containing the results.
Jobs can run in parallel when they do not depend on one another. This can reduce the time required to complete the overall process.
Another advantage is visibility. Contributors can see whether their changes passed the required checks without contacting another team member or waiting for a manual review.
For growing projects, github actions can provide a repeatable foundation for maintaining code quality. Teams can establish common standards and apply them consistently to different branches and contributors.
The result is a development process where problems are discovered closer to the moment they are introduced.
5. Moving from Continuous Integration to Continuous Delivery
Testing is only one part of releasing software. Once an application has passed its checks, developers still need to prepare a build and make it available to users.
Continuous delivery extends the automation process beyond integration. It helps prepare software for release whenever the required conditions are satisfied.
Continuous deployment takes this further by automatically publishing approved changes to a production environment.
These approaches reduce the number of manual operations involved in releasing software.
A typical deployment workflow might perform the following activities:
- Check whether the latest code has passed testing.
- Install the production dependencies.
- Generate an optimized application build.
- Prepare the necessary deployment files.
- Authenticate with the hosting provider.
- Publish the updated application.
- Verify that the deployment completed successfully.
The exact steps depend on the technology being used. A static website, a containerized application, and a backend service may all require different deployment procedures.
With github actions, developers can connect these stages through a single workflow. They can also use environment protections to require approval before deploying to production.
This is particularly important for applications where an unexpected release could interrupt important services.
A well-designed delivery process should include clear permissions, reliable testing, and a way to recover when something goes wrong.
6. Using Reusable Actions to Save Development Time
Not every automation task needs to be created from the beginning. Many common operations already have reusable actions available in the GitHub ecosystem.
These actions package specific operations into components that developers can include in their workflows.
For example, checking out repository files, setting up a programming language, caching dependencies, and publishing artifacts are common requirements. Reusable actions can simplify these operations and reduce repeated configuration.
Developers can find actions through GitHub Marketplace, where publishers provide tools for different development activities.
However, selecting an action requires some attention. Not every available component is equally reliable or suitable for every project.
Before adding an action, developers should examine:
- Who maintains the action.
- Whether it receives regular updates.
- Its documentation and supported configuration.
- The permissions it requests.
- Whether its source code is publicly available.
- Whether it meets the project’s security requirements.
It is also important to use trusted versions rather than automatically accepting every update.
Reusable workflows provide another way to reduce duplication. Organizations managing several repositories can create a shared workflow and reuse it across different projects.
This means teams do not need to maintain separate versions of similar automation instructions.
When used carefully, reusable components make github actions easier to scale while keeping project configuration manageable.
7. Protecting Secrets and Managing Workflow Permissions
Automation often needs access to external services. A deployment process might require a cloud credential, while another workflow may need permission to publish a package.
Storing sensitive information directly inside a workflow file is dangerous because repository files may be visible to other contributors or become part of the project’s history.
GitHub provides secrets and variables to help manage this information.
Secrets are designed for sensitive values such as access tokens, passwords, and credentials. Workflows can reference these values without placing the actual information directly inside their configuration files.
For example:
steps:
  - name: Deploy application
    run: ./deploy.sh
    env:
      DEPLOY_TOKEN: ${{ secrets.DEPLOY_TOKEN }}
The workflow receives the secret through an environment variable rather than displaying its actual value in the YAML configuration.
Permissions also deserve attention. A workflow should receive only the access required to complete its assigned tasks.
Using broad permissions unnecessarily increases the potential impact of a security problem.
Developers should review the permissions available to each workflow and restrict access whenever possible. They should also be careful when using third-party actions, particularly in workflows that process contributions from outside collaborators.
For cloud deployments, short-lived credentials through OpenID Connect can offer an alternative to storing long-term cloud access keys.
Security is not something that should be added only after automation becomes complicated. It should be considered during the initial design of every workflow.
8. Managing Dependencies and Build Artifacts
Modern applications frequently rely on external packages and libraries. These dependencies must be installed before an application can be tested or built.
Repeatedly downloading the same packages can make workflows slower than necessary.
Dependency caching helps address this problem. Instead of retrieving everything during every execution, a workflow can reuse previously stored dependencies when the relevant configuration has not changed.
The cache key usually depends on information such as the operating system and dependency lockfile. When those details change, the workflow can create or retrieve a different cache.
Another important concept is the build artifact.
An artifact is a file or collection of files generated during workflow execution. It might contain compiled application files, test reports, documentation, or packaged software.
Artifacts are useful because one job can generate files that another job needs later.
For example, a build job can create an application package, while a separate deployment job retrieves that package and publishes it.
This separation makes workflows easier to organize and can prevent unnecessary rebuilding.
With github actions, teams can configure artifact storage and retention according to their project requirements.
Good dependency and artifact management improves efficiency while making the development process easier to reproduce.
9. Improving Team Collaboration Through Pull Request Automation
Pull requests are an important part of collaborative development. They allow contributors to propose changes, discuss implementation details, and review modifications before merging them into a shared branch.
However, reviewing every detail manually can become time-consuming, especially in active repositories.
Automation can help by performing routine checks whenever a pull request is created or updated.
For example, a workflow might verify that required files exist, check code formatting, run tests, or generate a preview build.
Teams can also automate labeling and notifications to help organize incoming contributions.
These operations make it easier for reviewers to understand the status of a proposed change.
Another useful approach involves using separate workflows for different types of activity. A documentation update may not require the same testing process as a major application modification.
Path filters and branch conditions can help determine which workflows should execute.
This avoids unnecessary operations and keeps feedback relevant.
When github actions is combined with a clear pull request policy, developers can create a more predictable review process. Contributors receive faster feedback, while reviewers can spend more time examining important architectural and functional decisions.
10. Handling Scheduled Tasks and Repository Maintenance
Not every automated task needs to begin with a code change.
Some operations are useful on a recurring schedule. Examples include generating reports, checking project health, updating documentation, and running maintenance scripts.
Scheduled workflows allow developers to execute these operations automatically.
For example, a repository might generate a weekly report showing the current state of its automated checks. Another project could run a scheduled script to identify outdated dependencies.
These tasks are useful because maintenance often gets postponed when developers become busy with feature development.
Automation creates a regular process that does not depend entirely on someone remembering to perform each activity.
Developers should still consider the limitations of scheduled execution. A scheduled workflow is not necessarily guaranteed to start at the exact minute specified, particularly when GitHub is experiencing high demand.
For important operations, the workflow should also handle failures carefully and provide useful notifications.
Scheduled automation is most effective when it solves a clearly defined maintenance problem rather than introducing unnecessary complexity.
11. Understanding Common Workflow Problems
Even well-designed automation can encounter problems. A workflow might fail because of an incorrect configuration, unavailable dependency, insufficient permission, or unexpected change in an external service.
Understanding common causes makes troubleshooting easier.
Incorrect YAML formatting
YAML relies on indentation and specific formatting rules. A misplaced space or incorrect structure can prevent a workflow from being interpreted correctly. Developers should validate configuration files before committing significant changes.
Missing dependencies
A workflow may work on one developer’s computer but fail on a fresh runner because required packages were never installed. Every dependency should be included in the automated setup process.
Permission errors
Some operations require repository access or permission to publish files. Developers should check workflow permissions and authentication settings when an operation fails unexpectedly.
Incorrect branch conditions
A workflow may not execute because its event configuration excludes the branch where the change occurred. Reviewing the trigger conditions can help identify this problem.
Unreliable external services
A deployment or testing step may depend on another service that is temporarily unavailable. Retry strategies can help with temporary failures, although they should not hide genuine application problems.
GitHub provides workflow execution logs that show which steps succeeded and where failures occurred.
These logs are valuable when troubleshooting because they provide information about the environment and commands used during execution.
A useful debugging strategy is to examine the first meaningful failure instead of focusing only on the final unsuccessful status.
12. Building an Automation Strategy That Can Grow
A common mistake is attempting to automate everything immediately. Large workflows with too many responsibilities can become difficult to understand, test, and maintain.
A better strategy is to begin with the activities that offer the greatest benefit.
For a small project, this might mean automatically running tests whenever code changes. Once that process is stable, developers can introduce build generation and deployment.
Larger teams may benefit from dividing automation into separate workflows according to responsibility.
For example, one workflow can handle testing, another can prepare releases, and a third can manage scheduled maintenance.
This separation makes troubleshooting easier because each workflow has a clearly defined purpose.
It is also worth documenting important decisions. Team members should understand why a workflow exists, which permissions it needs, and what happens when it fails.
Monitoring execution time can help identify inefficient steps. Dependency caching, parallel jobs, and appropriate runner selection may reduce unnecessary delays.
A scalable setup should remain understandable as the repository becomes larger.
The purpose of github actions is not simply to create more automation. It is to remove repetitive work while maintaining control over important development decisions.
13. Why Workflow Automation Matters for the Future of Software Development
Software development continues to evolve as applications become more connected and teams adopt increasingly diverse technologies.
Developers now work with cloud platforms, containers, APIs, automated testing frameworks, and distributed services. Managing all these components manually can create unnecessary operational pressure.
Automation provides a way to connect these activities into a consistent development process.
GitHub Actions is useful because it places automation close to the code and collaboration tools developers already use. Teams can manage workflow definitions alongside their application files, review configuration changes, and track execution history within the same platform.
This makes automation part of the development process rather than a completely separate responsibility.
It also supports experimentation. Developers can test new ideas in individual branches without immediately changing the production environment.
As projects mature, they can introduce more advanced practices such as deployment approvals, reusable workflows, security checks, and environment-specific configurations.
The most successful approach is to keep automation purposeful. Every workflow should solve a real problem, provide useful feedback, or reduce unnecessary manual effort.
Conclusion
Building software involves a continuous series of activities, from writing the first lines of code to testing, reviewing, and releasing an application. Handling these operations manually can slow development and introduce avoidable mistakes.
GitHub Actions offers developers a practical way to connect these stages through automated workflows. It supports continuous integration, testing, build generation, deployment, scheduled maintenance, and collaboration-related tasks.
The best place to begin is with a small workflow that solves an immediate development challenge. Once it works reliably, additional operations can be introduced gradually.
By combining reusable actions, appropriate security controls, clear workflow structures, and meaningful testing, developers can create processes that remain manageable as their projects grow.
Ultimately, github actions helps turn repetitive development activities into consistent automated processes, giving teams more time to focus on building useful software and delivering better experiences to their users.
